Time to expand my old Proxmox configuration, which served me well for the past two years, with a new public IP, a cloud router, and a separate private subnet.. The goal:
- Keep old existing IP, subnet, DHCP, etc
- Keep controlling proxmox from old IP
- Add a new Public IP, new private subnet
- Install some easy to manage cloud router, iptables is so painful.
Oneprovider delivers failover IPs – ARP based, which means that static IP with exact MAC address will be used. Only 1 NIC. Every router needs at least 1 WAN & 1 LAN. WAN will connect directly to Public vmbr0 bridge. New vmbr3 will be created and used for LAN. Public failover IP: 123.123.123.123
Network diagram
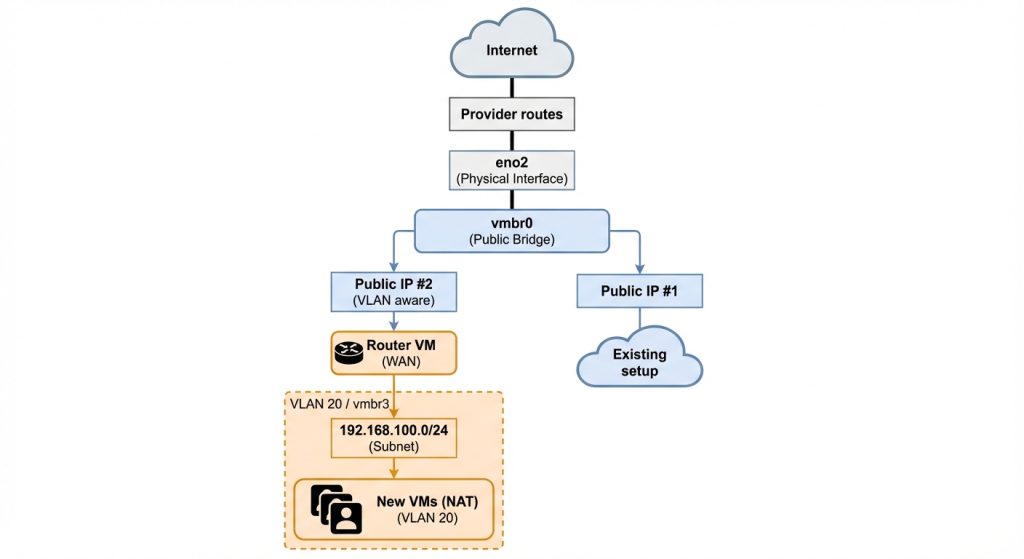
/etc/network/interfaces will be changed in order to meet new requirements. Just add new vmbr3 bridge and replace port forwarding from vmbr0 to static IP. Config looks like this:
auto lo
iface lo inet loopback

iface eno1 inet manual
iface eno2 inet manual

# Main public interface/ 202.202.202.202 is the old ip
auto vmbr0
iface vmbr0 inet static
        address 202.202.202.202/24
        gateway 202.202.202.1
        bridge-ports eno1
        bridge-stp off
        bridge-fd 0

# Internal VM network. 10.10.10.0/24 is the old subnet
auto vmbr2
iface vmbr2 inet static
        address 10.10.10.1/24
        bridge-ports none
        bridge-stp off
        bridge-fd 0

        # Enable IP forwarding
        post-up echo 1 > /proc/sys/net/ipv4/ip_forward

        # Masquerade outgoing traffic from VM network
        post-up iptables -t nat -A POSTROUTING -s 10.10.10.0/24 -o vmbr0 -j MASQUERADE
        post-down iptables -t nat -D POSTROUTING -s 10.10.10.0/24 -o vmbr0 -j MASQUERADE

        # Connection tracking for FW bridges
        post-up iptables -t raw -I PREROUTING -i fwbr+ -j CT --zone 1
        post-down iptables -t raw -D PREROUTING -i fwbr+ -j CT --zone 1

        # DNAT for UDP 55520 to specific VM
        post-up iptables -t nat -A PREROUTING -d 202.202.202.202 -p udp --dport 55520 -j DNAT --to-destination 10.10.10.15:55520
        post-down iptables -t nat -D PREROUTING -d 202.202.202.202 -p udp --dport 55520 -j DNAT --to-destination 10.10.10.15:55520

        # DNAT for TCP 443 ONLY to the main IP
        post-up iptables -t nat -A PREROUTING -d 202.202.202.202 -p tcp --dport 443 -j DNAT --to-destination 10.10.10.7:443
        post-down iptables -t nat -D PREROUTING -d 202.202.202.202 -p tcp --dport 443 -j DNAT --to-destination 10.10.10.7:443

# Optional extra bridge (VLAN aware)
auto vmbr3
iface vmbr3 inet manual
        bridge-ports none
        bridge-stp off
        bridge-fd 0
        bridge-vlan-aware yes
bridge-vids 20List old iptables
iptables -t nat -L PREROUTING -n -v --line-numbersDelete old rules. 1 is the first rule. After deleting a rule, line numbers shift. If you have more to delete, re-list first.
iptables -t nat -D PREROUTING 1
apply configuration
ifreload -aCreate new VM with two network interfaces. Deactivate proxmox build in firewall. We will use the router as firewall.
- WAN -> vmbr0. Use MAC provided from cloud!
- LAN -> vmbr3. VLAN tag: 20
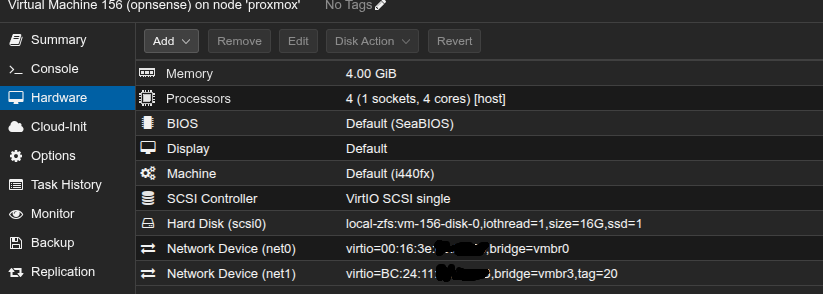
Install opnsense. When updating it, use http, not https, in FreeBSD repos.
